

My posts here at the Lint Trap have gotten lengthy. Perhaps you’ve noticed?
And they’ve been troubling me for other reasons. For example, recent posts, on early radio research, John Tunis’ Was College Worth While? (1936), and Bari Weiss’s travails at CBS News, would’ve made good pitches to outlets like Boston Globe Ideas, The Conversation, The Atlantic, or Slate. If they’re published by professional outlets, I get more credit from my employer, more reads, more respect… even if the labor involved, and final product, are somewhat similar.
So today’s post is going to (hopefully?) be brief. I was recently listening to a colleague doing a great job on the radio program “Maine Calling” discussing media literacy, AI, social media, and the concept of “digital trails.” A listener asked the experts whether smartphones are listening to off-line conversations. The listener described that uncanny feeling - the creepy suspicion I think we all share - when they would say something in conversation and the next time they ventured online their screen would be flooded with ads drawn from their off-line spoken words.
That question reminded me of something I intended to post about: The class action lawsuit of Lopez v. Apple, which was settled earlier this year (2025).
You can read all about Lopez v. Apple in much of the media coverage. Or you can ask for an AI summary of it from Google.
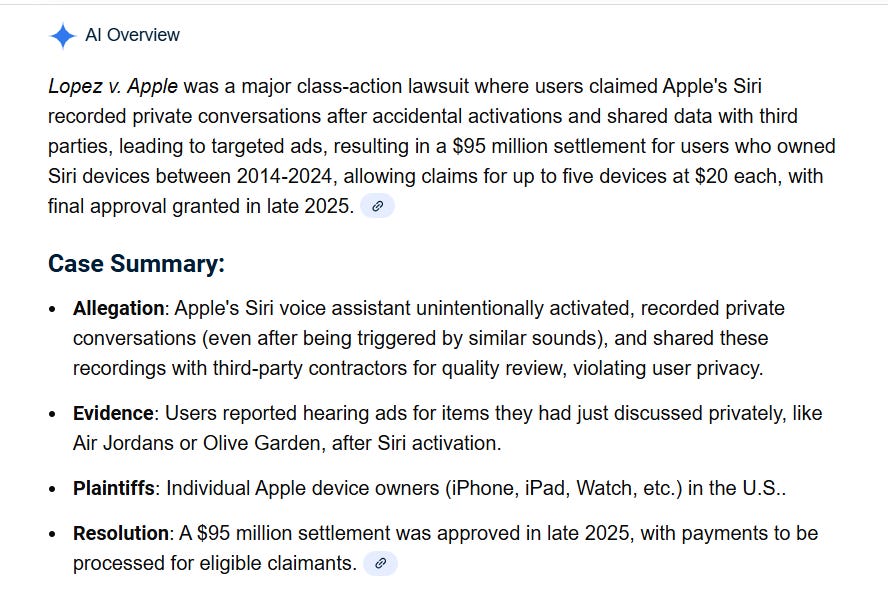
The bottom line is this: Apple settled for $95 million (plus attorneys fees) in exchange for the ability to deny culpability.
That’s a great deal for Apple. For just about $100 million, they get to clean up one of the most serious allegations of privacy invasion they ever faced. Things were looking bad for them as the case progressed. At one point, the judge sanctioned Apple for “accidently” deleting recordings relevant to the lawsuit. Whether or not those recordings might’ve informed the public of the scope of Siri’s surreptitious listening, we’ll never know. But we do know the settlement means we’ll never find out.
So it turns out that yes, Siri does (did?) listen to you.
If you spoke so-called “hot words,” or pronounced words that sounded like “Siri” (examples in the case included “Syria” and “seriously”), Siri would engage. With Siri thus activated, it would listen. It would then sell your ensuing spoken conversational data to commercial advertisers, and you’d then see targeted ads on your phone and laptop. Apple termed these events “false activations” and admitted they occurred. But we have no idea how often these activations would happen.
Back in 2019, Apple was a bit more forthcoming about how it employed brief surreptitious Siri recordings in order to better train its AI. A contractor working on the project blew the whistle and went to the press to explain how this was being done.
I guess whether you believe these Siri listening issues have truly been “accidental” or intentional will be based upon your confidence that Silicon Valley corporations act in accordance with regulations and their own privacy protection policies. For me, the decades of apologies, and enormous fines, have eroded my confidence in Meta, Google, Apple, Tik Tok, and the rest, to behave with consistent ethics or morals. These privacy cases just keep happening - for example, how many of you knew about this recent verdict?
In September [2025], a federal jury in California found Google liable on two counts of privacy violations for continuing to collect the data of millions of users who had turned off a data tracking setting in their Google Accounts. Google has to pay $425 million for the privacy violations.
Google denies the allegations in the lawsuit and is appealing the verdict.
As this Reuters article notes, Google has a long history of lying about privacy. “Google has faced other privacy lawsuits, including one earlier this year where it paid nearly $1.4 billion in a settlement with Texas over allegations the company violated the state’s privacy laws. Google in April 2024 agreed to destroy billions of data records of users’ private browsing activities to settle a lawsuit that alleged it tracked people who thought they were browsing privately, including in ‘Incognito’ mode.”
The truth is always complicated. It’s entirely reasonable to believe the eerie feelings evoked by our phones and computers seemingly being able to read our minds is the result of precision targeting. The data being collected and analyzed has reached unthinkable levels of sophistication, and, candidly, I’m largely persuaded that’s actually what’s going on. But that doesn’t mean our phones don’t listen to us occasionally as well. Those two possibilities aren’t mutually exclusive. In fact, they’re symbiotic.
If there can be a backdoor or a way to skirt the regulations, they will take advantage of it. The only way we find out such things are if the hacker class finds a reason to really dig into it. Openish source architecture like Android based devices allow for it to be less impossible to investigate such things, but Apple's proprietary architecture makes it nearly impossible. You can just watch API calls and other network traffic that moves over the network... then make educated guesses.
If you think this behavior has stopped due to a no-fault ruling... let's just say, no way.